Cyber Resilience Act software
CRA Compliance Cockpit for product cybersecurity readiness
Know whether the CRA applies, where your organisation and products fall short, and what to close before the deadlines, with evidence an auditor can follow.
- EU 2024/2847
- SBOM
- VEX
- CISA KEV
- Article 14
- Conformity
Product
What the cockpit covers
For software, hardware, IoT and OT manufacturers worldwide placing products with digital elements on the EU market.
- 01
Product intake and classification
Product context, operator role, scope and classification with traceable rationale.
- 02
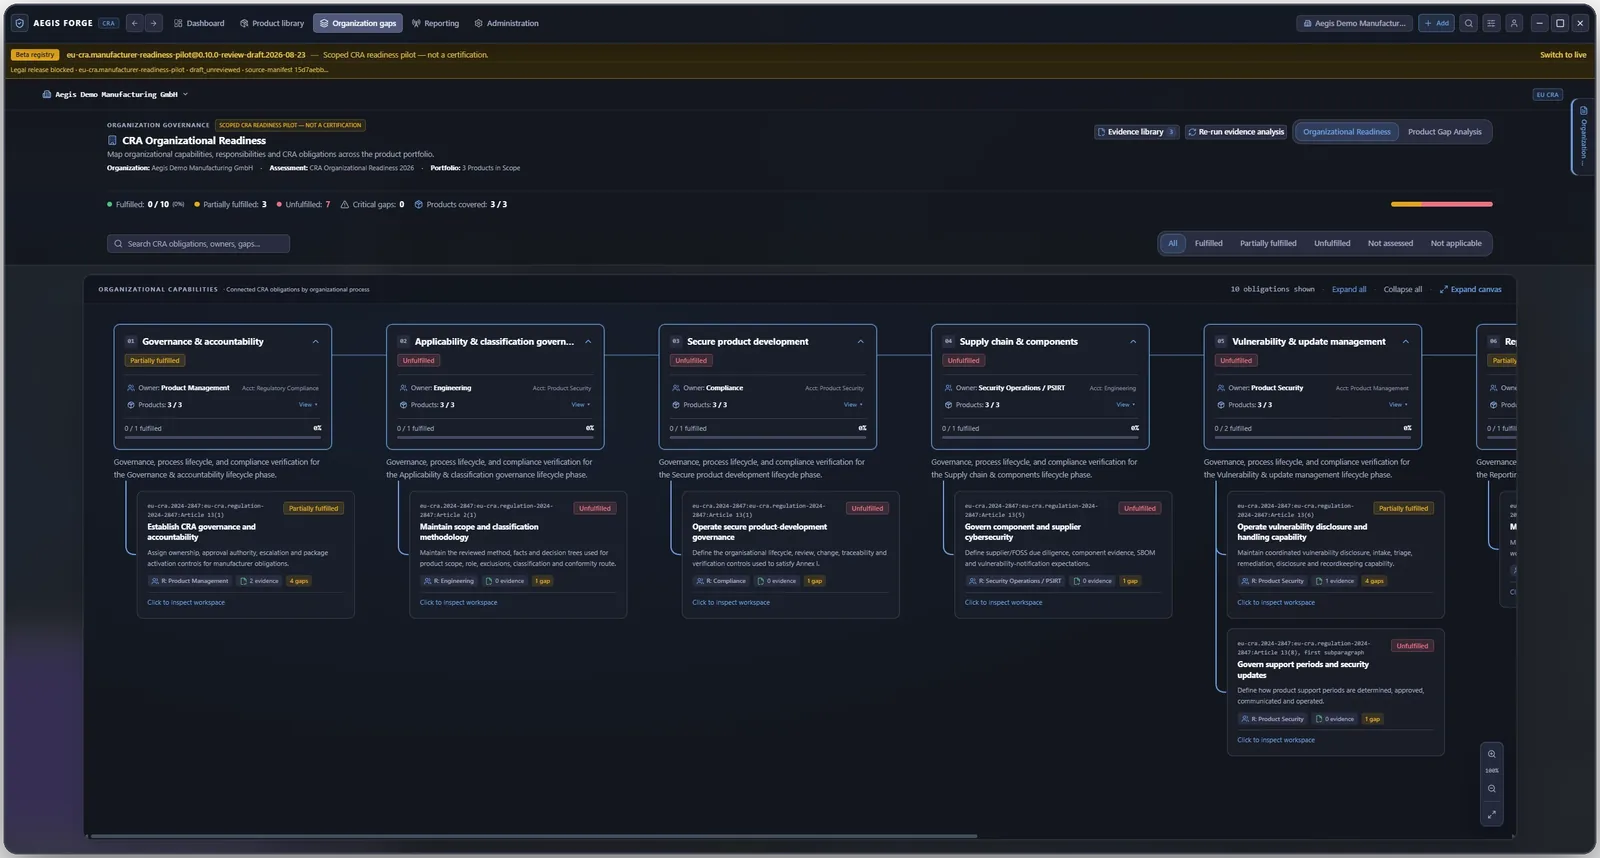
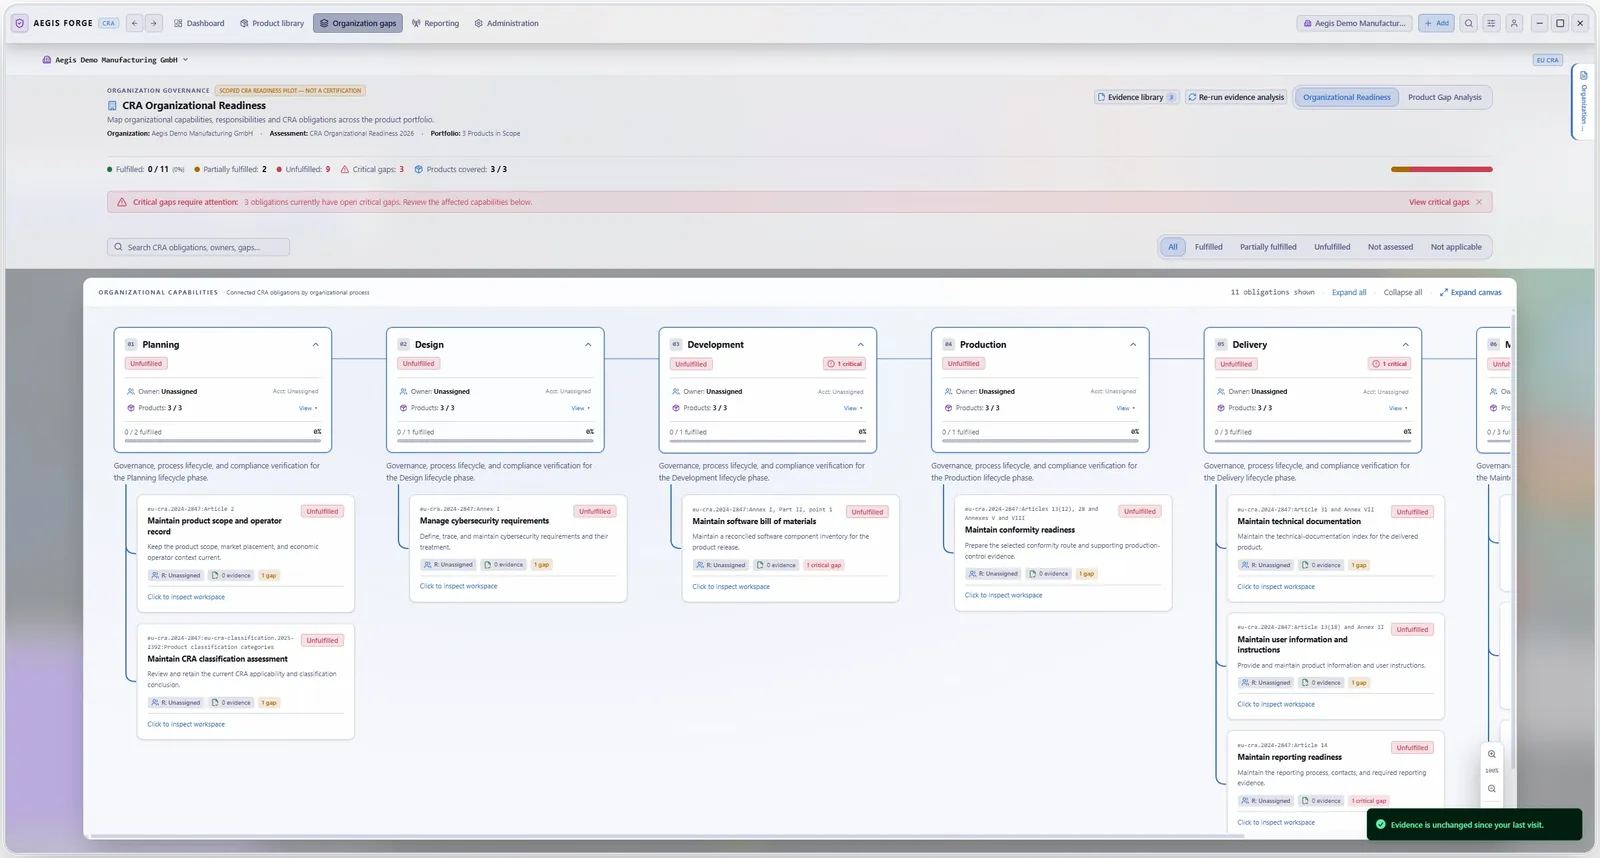
Organisation and product readiness
Organisational capabilities, product obligations and gaps across your portfolio.
- 03
Evidence and AI proposals
Map documents to obligations, inspect sources and accept proposals under human control.
- 04
SBOM and vulnerabilities
Components, vulnerability findings, impact assessments and VEX in product context.
- 05
Remediation and release readiness
Connect gaps to owners and remediation; prepare conformity records and audit exports.
- 06
Post-market and reporting
Vulnerability and incident cases, deadlines and reporting packages. Authority submissions are filed separately.
Scope, rule package, data sources and deployment are confirmed in the pilot. Conformity assessment and authority reporting remain with the manufacturer.
Product views
From product intake to Article 14 reporting
Current screens with a synthetic demo manufacturer.
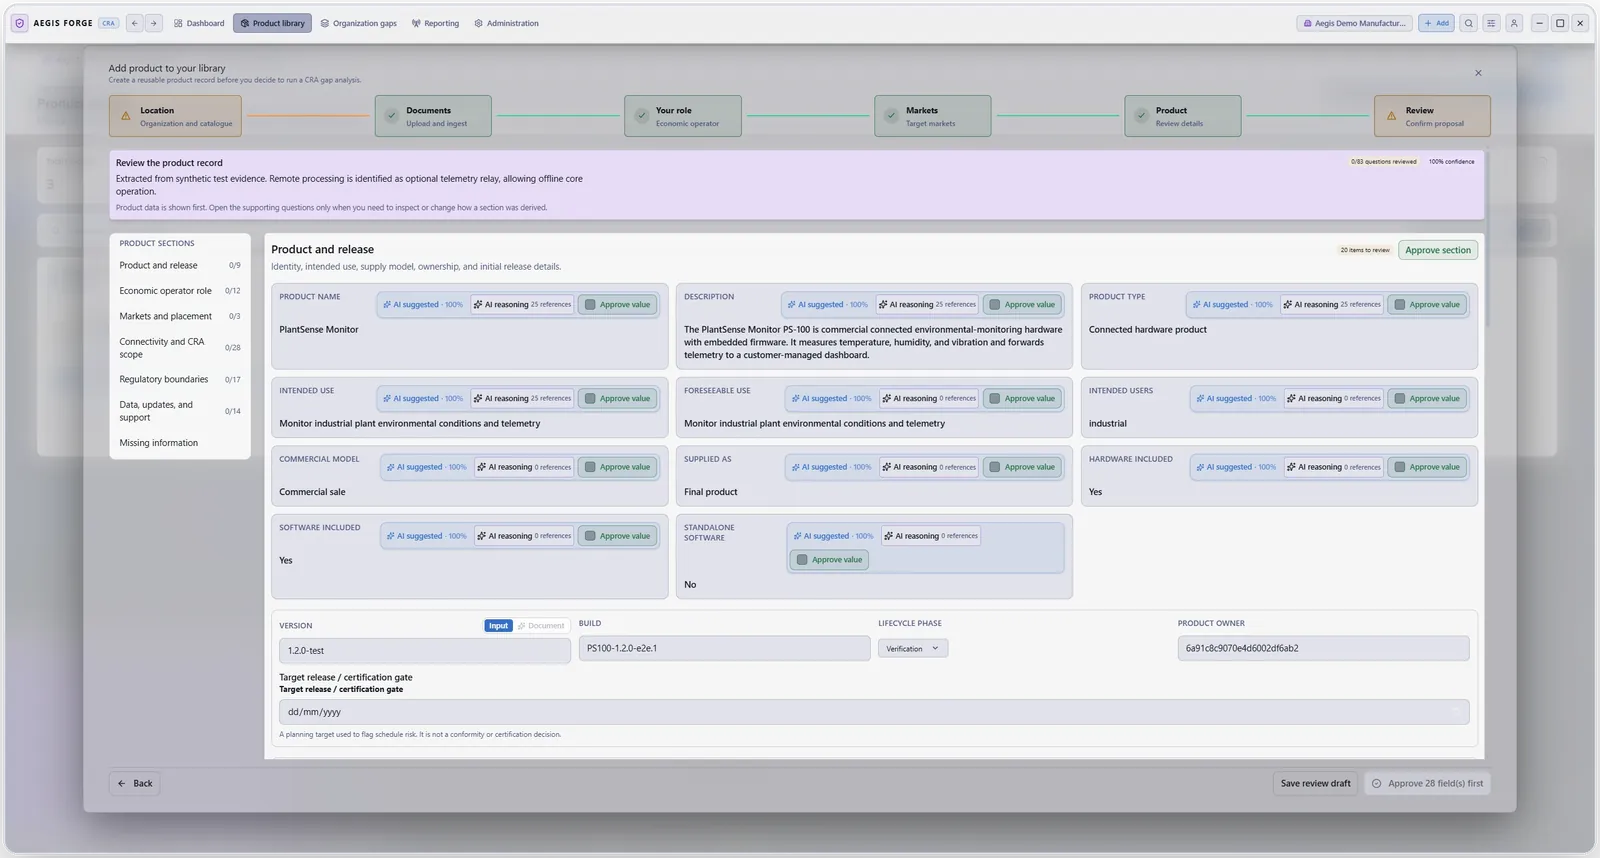
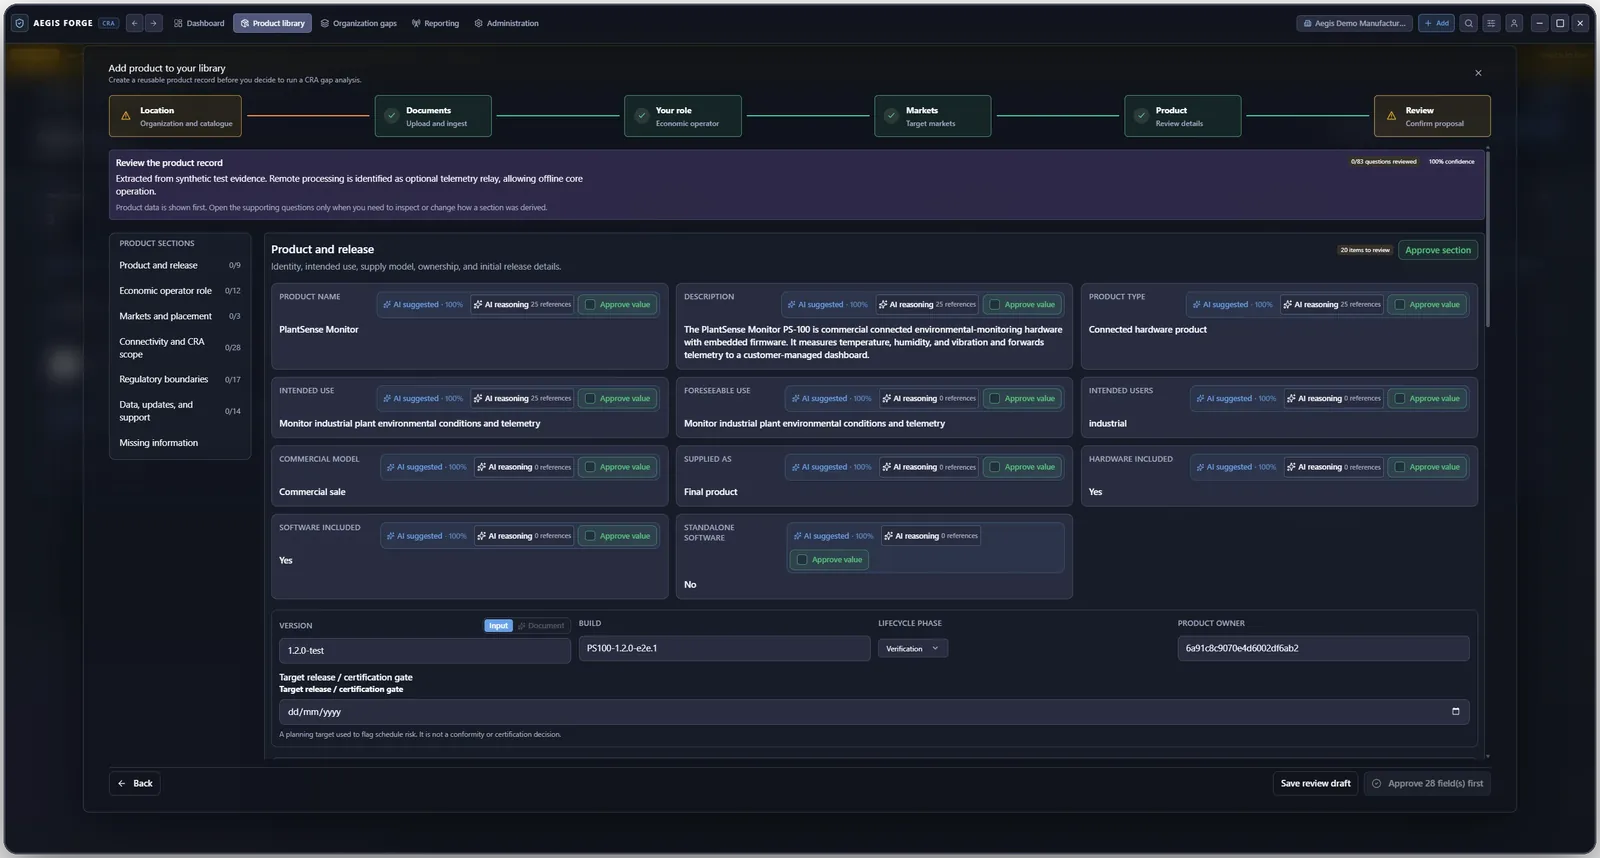
01/10AI-assisted product intake
Suggested product facts with reasoning references; each value is approved before classification.
Cockpit loop
Six steps, one evidence trail
- 01Define product
- 02Classify scope
- 03Review evidence
- 04Triage vulnerabilities
- 05Close gaps
- 06Prepare reporting
CRA self-check
Does the CRA apply to your product? Check in 2 minutes.
Deterministic scope rules, no AI. The full CRA Cockpit analysis then connects product data, SBOM, evidence and obligations.
Result · CRA relevance
Check Default or Important Class I
Self-check only, not legal advice and not a conformity guarantee.
Your role
- 01
Is the product software, hardware with digital elements, or a connected product?
- 02
Is it placed on the EU market, supplied to EU customers, or planned for EU release?
- 03
Is it offered commercially or as part of a business activity?
- 04
Is it clearly covered by a specific excluded sector regime or purely non-commercial open source?
- 05
Does it provide security, identity, network, update, access-control, or vulnerability-management functions?
- 06
Does the product depend on remote processing, cloud services, APIs, or continuous updates?
FAQ
Frequently asked questions
Does the CRA Cockpit certify a product?
No. The cockpit supports readiness, evidence and review. Conformity assessment and legal decisions remain with the responsible manufacturer and qualified assessors.
Can manufacturers outside the EU use the cockpit?
Yes. The offering is relevant to manufacturers placing products with digital elements on the EU market. Product scope and economic operator responsibilities are confirmed during assessment.
Does the cockpit submit reports to authorities automatically?
It supports case management, deadlines and reporting-package preparation. Reports must be reviewed and submitted through the applicable authority process.
Walk through the CRA Cockpit with one of your products.
Compliance work stays connected to engineering traceability in ASF Core. We reply within one business day.